At Pegamento, technology is all about people: customers who want excellent service, employees who rely on their systems, and organizations for which accessibility, privacy, and security are essential.
That’s why we consistently prioritize information security, data protection, and business continuity. We work according to recognized standards, undergo independent audits, and have clear agreements regarding our services.
In this Trust Center, we show how we approach this: transparently, clearly, and with a focus on what it means for your organization.
Every day, people entrust their data to organizations—whether by phone, email, chat, or other digital channels. That information deserves strong protection.
At Pegamento, we understand how important this is—especially for organizations in healthcare, government, social services, and other sectors where sensitive data and accessibility go hand in hand. That’s why information security isn’t a standalone project, but an integral part of everything we develop, manage, and support.
We take concrete measures and have our practices independently audited. That way, you don’t have to rely solely on our word.
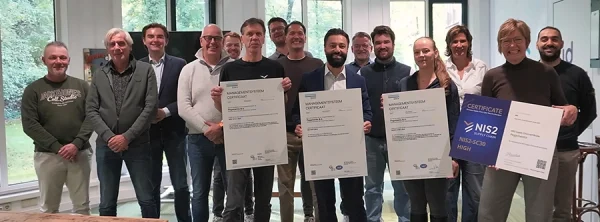
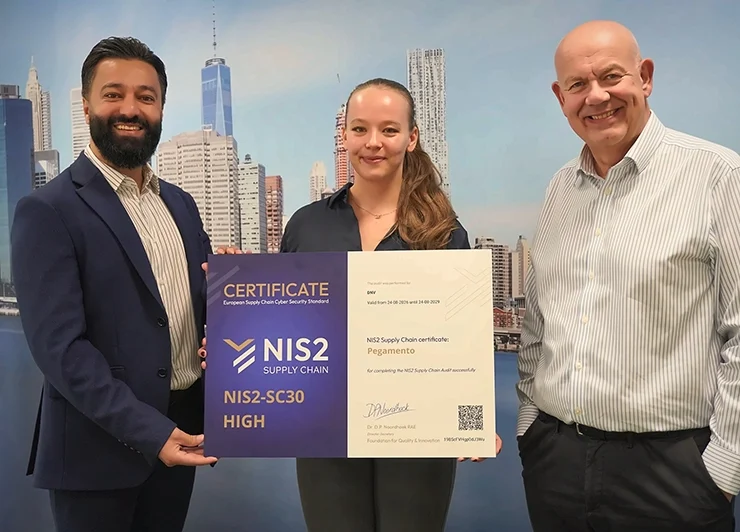
Our information security management system is certified to ISO 27001 and is audited annually by DNV. For clients in the healthcare sector, we comply with NEN 7510, and for government clients, we operate in accordance with the Government Information Security Baseline (BIO 2.0). In addition, we have achieved the NIS2 SC30 High assessment.
Our control measures are also independently assessed through ISAE 3000 and ISAE 3402 reports, including a SOC 2 Type II audit. We would be happy to explain which statements and reports pertain to a specific service or period.
Certification and assurance: what’s the difference?
Certification confirms that a management system, within a specific scope, meets the requirements of a standard. An assurance report provides independent insight into specific control measures; in a Type II audit, the effectiveness of those measures over a specific period is also assessed. These two forms of assessment complement each other.
Would you like to see for yourself what our findings are based on? You can request a summary of the relevant reports using the form below.
Effective security consists of multiple layers: from the infrastructure to the employees who work with it.
Access Based on Need
Employees are granted access only to the systems and data they need for their work. Logins require multi-factor authentication (MFA), and we review access rights quarterly.
Encryption
Data is stored and transmitted in encrypted form.
Secure hosting
Our platforms run in ISO 27001-certified data centers in the Netherlands. We assess the security level of partners such as Uniserver and Sprinklr both initially and on a regular basis. For each solution, we clearly specify the applicable infrastructure and processing agreements.
Monitoring and Detection
We monitor our systems 24/7 for anomalous behavior and suspicious activities, with support from Reqon.
Patch and Vulnerability Management
We implement critical security updates within two days. Our environment is tested annually by an independent penetration tester.
Secure Development
For custom development—for example, in Mendix—we follow secure-by-design principles and conduct code reviews.
Technology alone is not enough. All our employees sign a confidentiality agreement and submit a certificate of good conduct (VOG). They complete mandatory annual security awareness training, including phishing simulations. This ensures that employees are aware of the risks and know how to handle information with care.
No organization can guarantee that an incident will never occur. The difference lies in preparation and how you respond. Pegamento has a documented incident response process, with clear roles and escalation lines.
In the event of a security incident affecting your data, we will notify you without undue delay and no later than 48 hours, in accordance with our agreements. We work together on recovery and, afterward, investigate which improvements are necessary.
Does your organization fall under NIS2 or DORA? We then provide support with relevant information for your own assessment and any reporting to regulators. Your specific legal reporting deadlines remain leading in this process.
Have you discovered a potential vulnerability in one of our systems? Please report it responsibly via [email protected]. We appreciate reports from security researchers and will ensure appropriate follow-up.
We’d be happy to help.
Schedule a 15-minute introductory meeting at
or call +31 (0)88 00 67 180
Deepen your knowledge with Pegamento’s white papers.